
Remote user enrollment
By design, Defguard Core is meant to be deployed securely within your infrastructure and only accessible from within the internal network or by VPN.
This introduces an issue with onboarding new users and forces the admin to choose an initial password, set up a VPN device for them, and pass on those details to the end user using possibly insecure channels.
To avoid this issue you can deploy a public Defguard Edge (formerly Proxy) which enables a secure enrollment process.
Here is a video showcasing:
how admin adds a user with secure remote enrollment
then how the enrollment process looks like for the user
How to initiate user secure enrollment
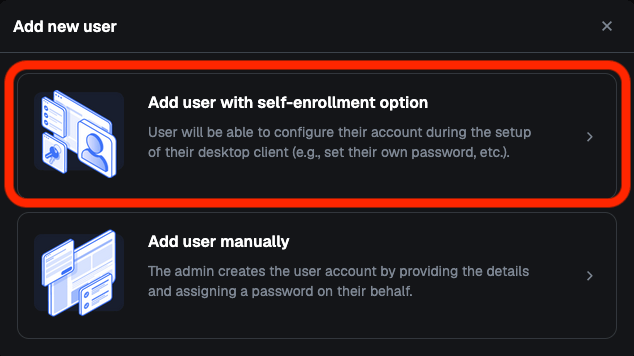
When adding a new user please choose "Add user with self-enrolment option"
If SMTP is configured, you will see "Send enrollment details to user by email" checkbox.
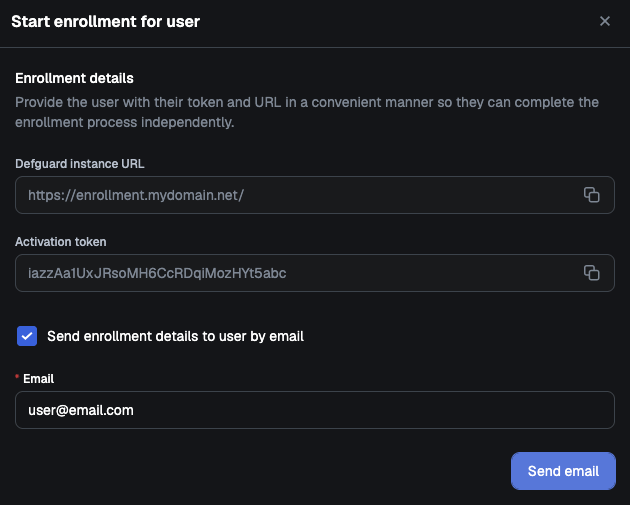
If you don't have any SMTP configuration, Defguard instance URL and Activation token must be handed over to the user personally.
When the user adds a Defguard instance in the Desktop client using the received token, not only is the VPN client configured, but the user can also:
set up their password
configure MFA, which is required to connect to MFA-protected locations
This means the user may not even have access to Defguard itself, but can still configure both VPN and MFA!
For MFA configuration to be mandatory during the enrollment process, there must be at least one VPN location with MFA enabled. Otherwise, MFA setup will remain optional.
Restarting enrollment manually
If there are any issues with the enrollment process (failed notification delivery, a lost token etc) you can restart it:
Go to Users page
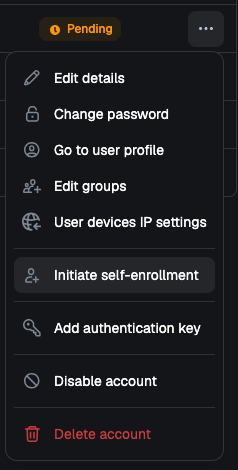
Find the relevant user and click on the "…" button on the right
An Initiate self-enrollment option should be available in the pop-over menu
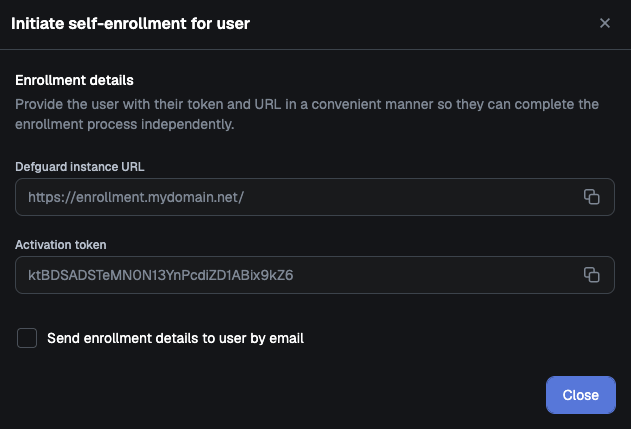
Clicking it will open the same modal as before.
Performing remote enrollment (as a user)
Obtaining token manually (e.g., via encrypted chat)
Go to Edge page
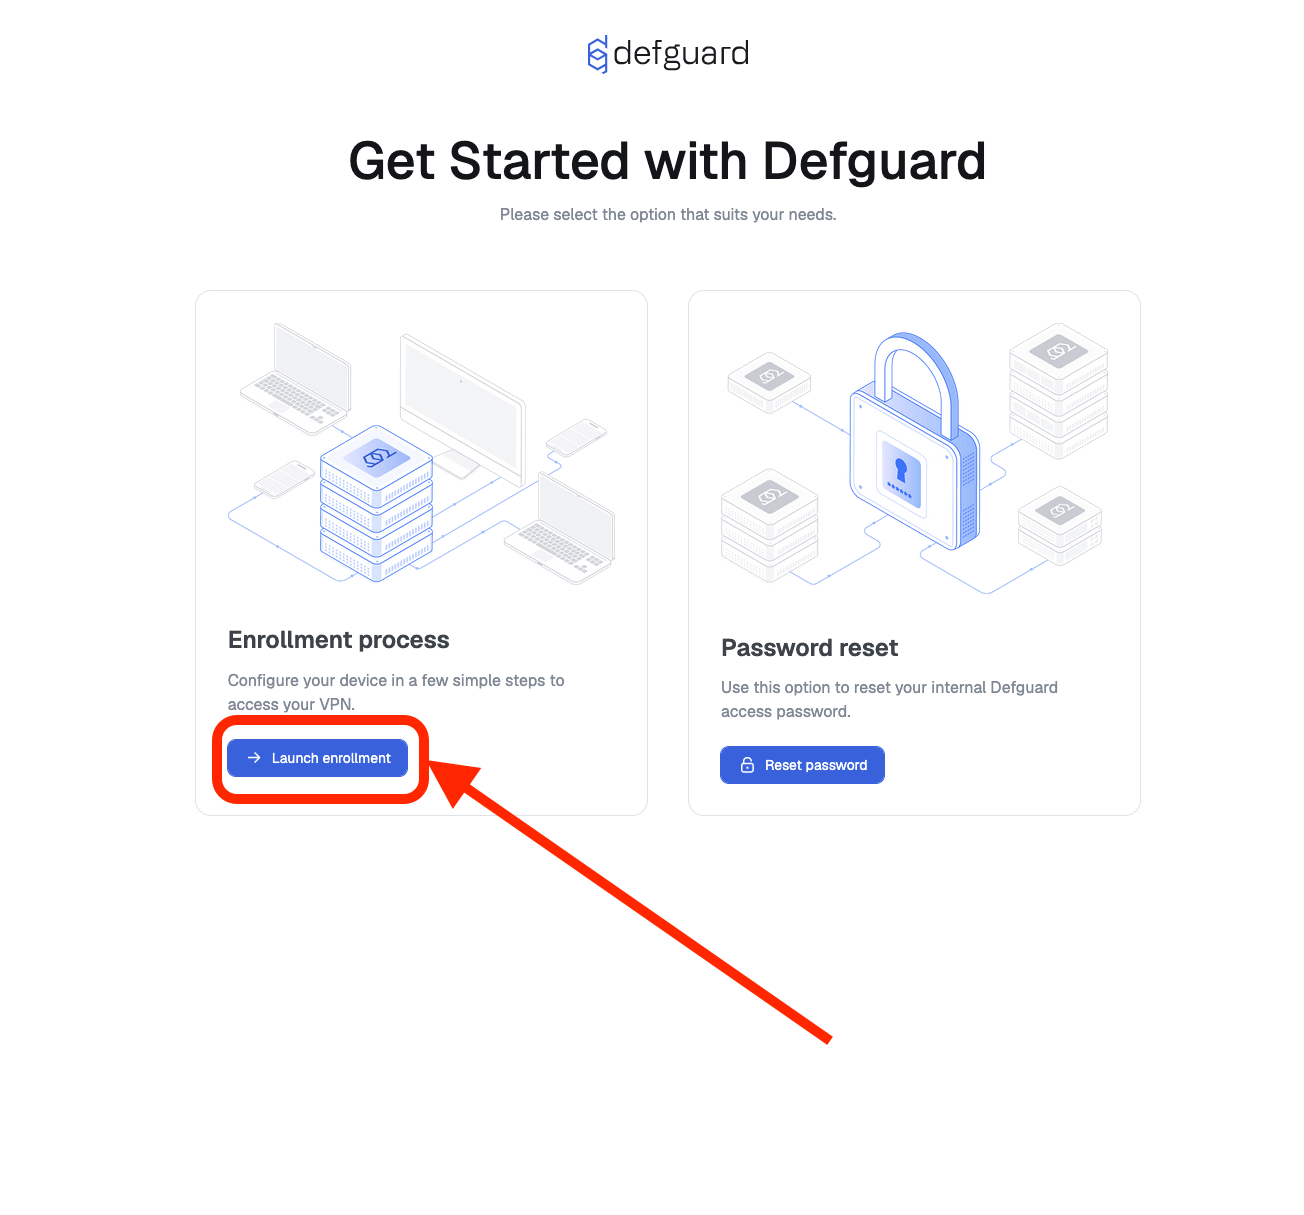
Enter your enrollment token and click "Continue" button
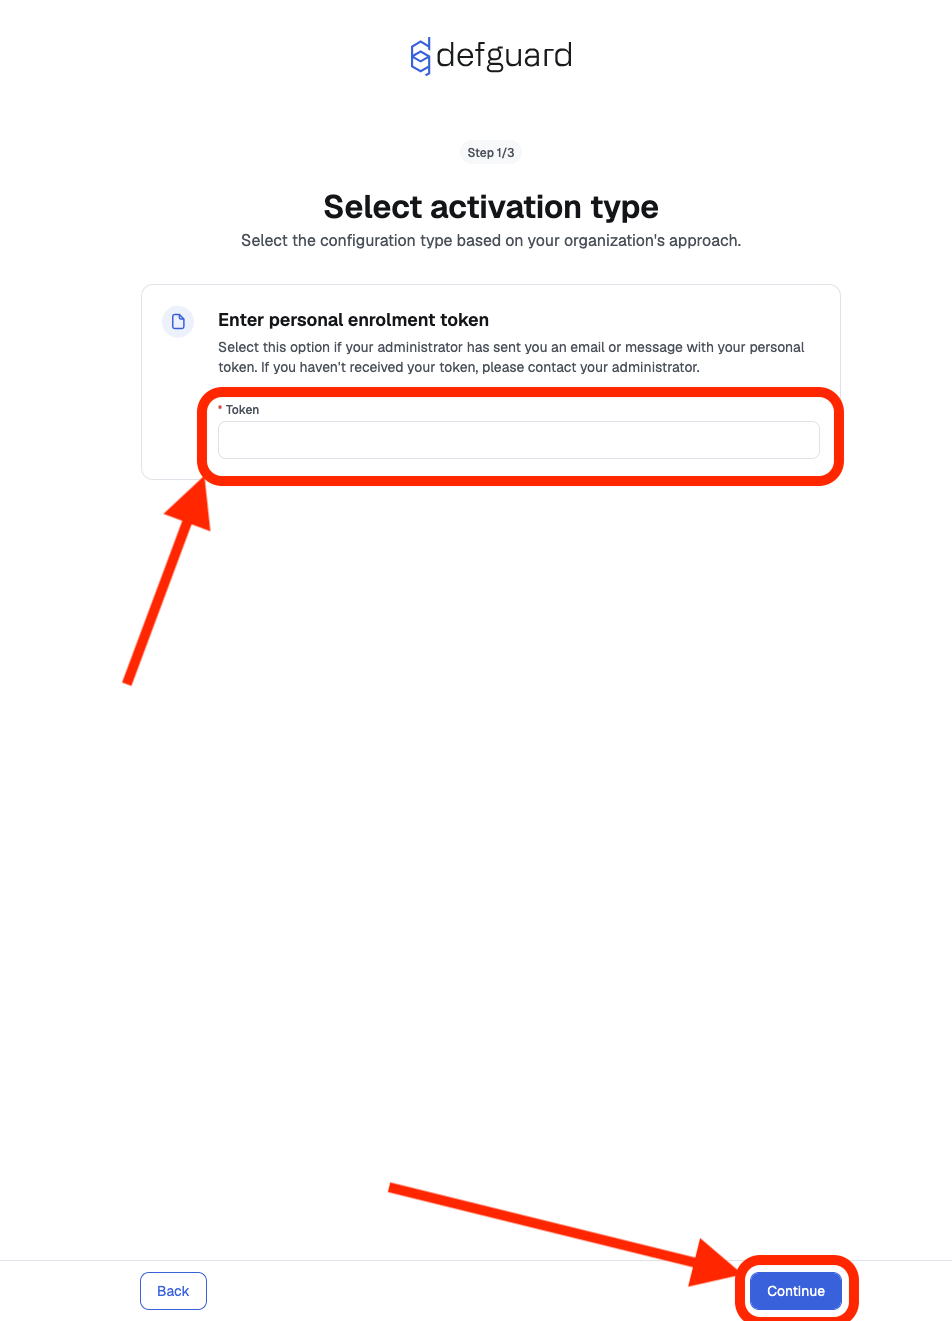
Download Desktop Client compatible with your Operating System.
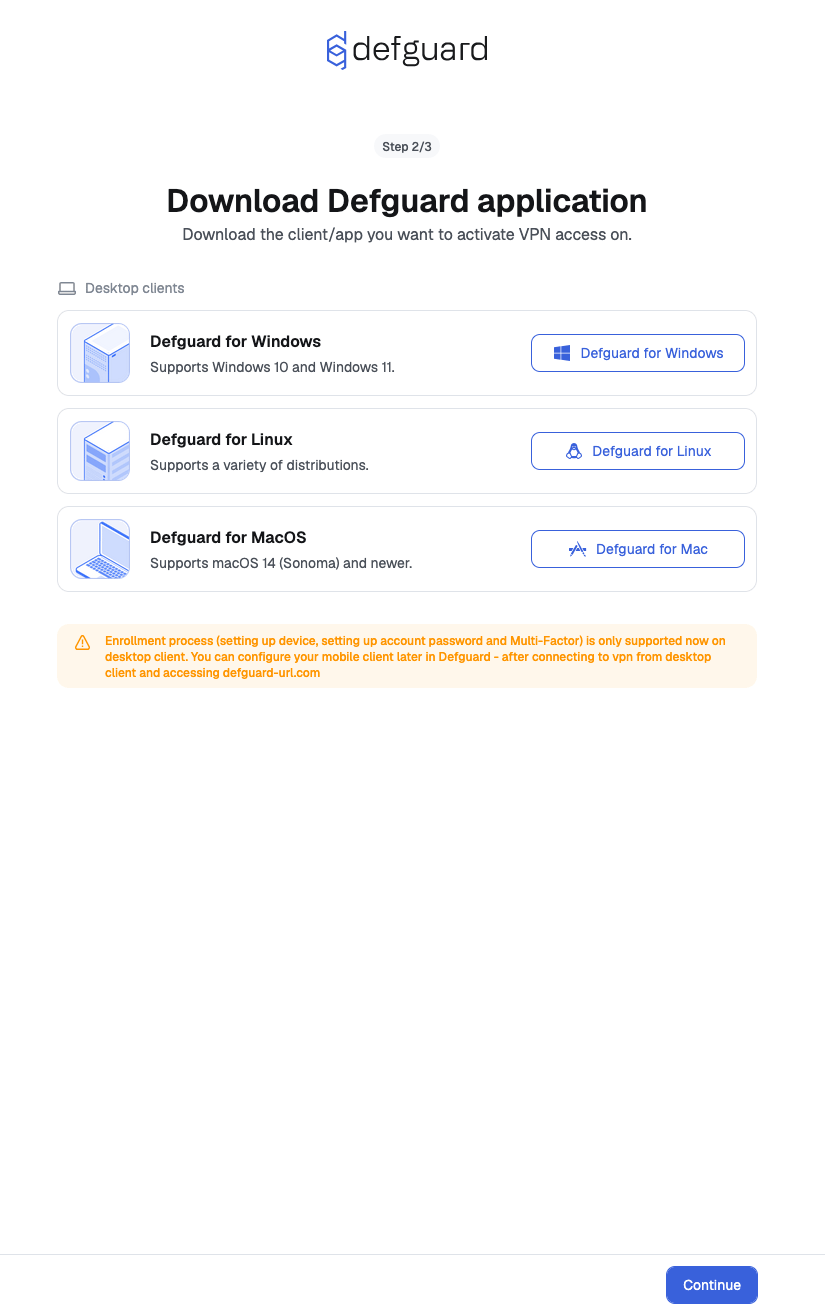
Now, enrollment can be performed in Desktop Client
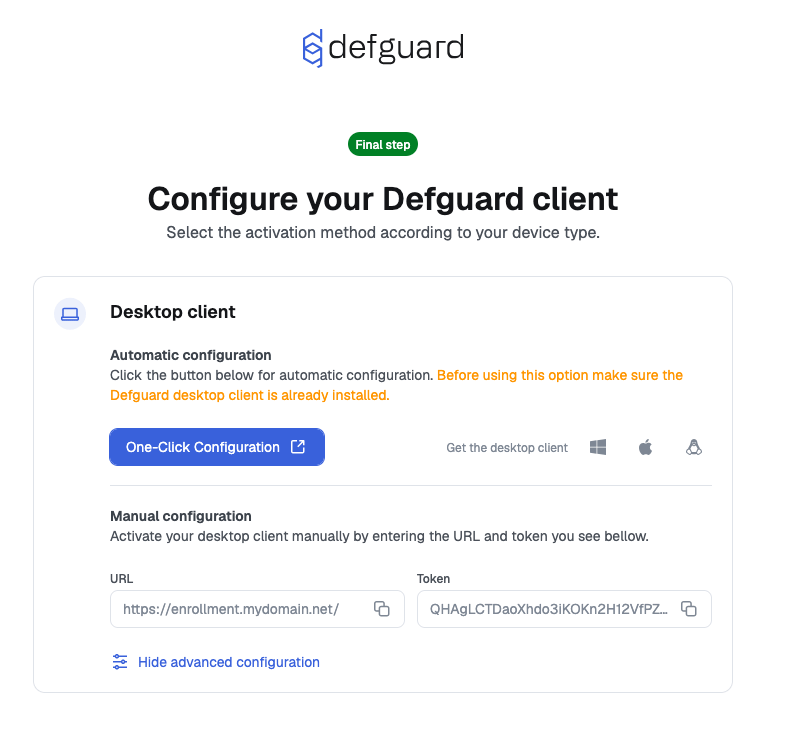
Now you can click "One-Click Configuration" which will open Desktop Client and enter credentials for you.
Obtaining token via email
Click "Enroll with desktop client", or copy
URL/Tokenmanually to Desktop Client
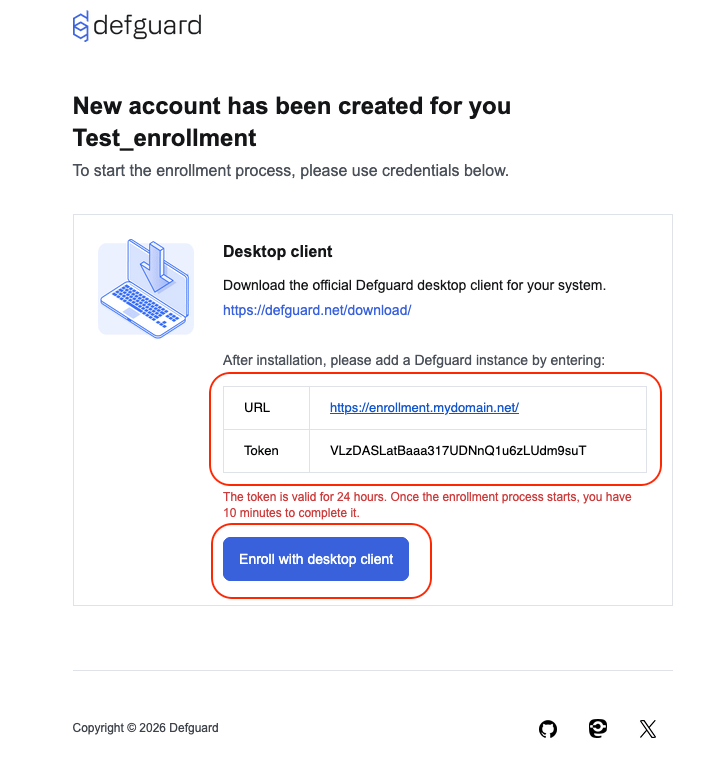
Entering URL/Token inside Desktop Client will trigger user enrollment process.

By following the enrollment wizard in Desktop Client, you'll be able to do the following:
verify that your data is correct
activate your user account
choose your password
setup MFA method
add an initial device for VPN access
After completing enrolment process, you will be able to connect to the VPN.
Enrollment settings
As an admin, you can configure enrollment-related settings on the Enrollment page. This includes:
Customizing the Edge UI settings
Setting token validity time
Enrollment session duration

Customizing the user onboarding messages.
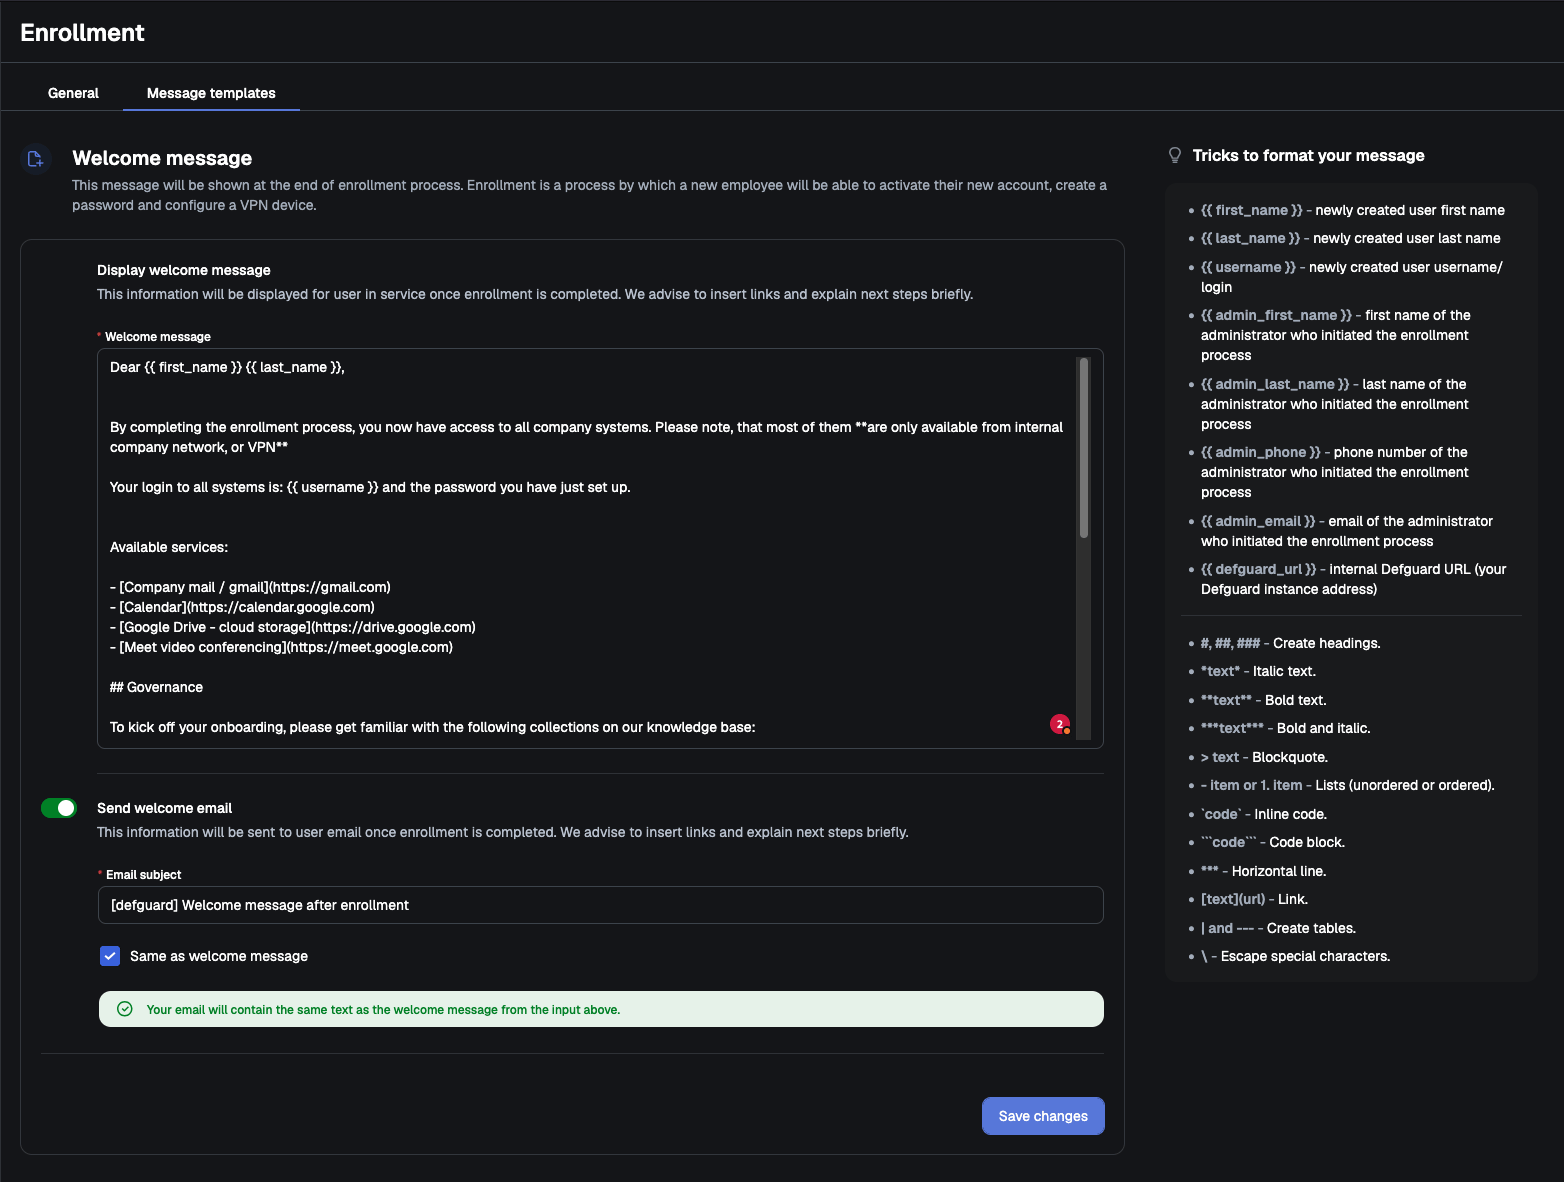
Message template tags
There are several template tags (similar to Jinja2 tags) that you can use in the onboarding messages to insert some dynamic content:
{{ first_name }}- newly created user first name{{ last_name }}- newly created user last name{{ username }}- newly created user username/login{{ admin_first_name }}- first name of the administrator who initiated the enrollment process{{ admin_last_name }}- last name of the administrator who initiated the enrollment process{{ admin_phone }}- phone number of the administrator who initiated the enrollment process{{ admin_email }}- email of the administrator who initiated the enrollment process{{ defguard_url }}- internal Defguard URL (your Defguard instance address){{ defguard_version }}- Defguard version
Edge UI settings
The Defguard proxy (Edge) serves a small public web interface to end users - the same page reached through the enrollment / onboarding link, which also offers self-service password reset. On the Enrollment settings page, under Edge UI Settings, you can hide parts of that interface your organization does not need.
Display the "Download client" page during enrollment
Enabled
Shows the step that lets users download the Defguard desktop client during enrollment. Disable it when the client is distributed centrally (for example via MDM or a software-distribution platform) so users are not prompted to download it themselves.
Display the "Reset password" option on the Enrollment Service home screen
Enabled
Shows the self-service password reset entry on the Enrollment Service home screen. Disable it when authentication is handled entirely by an external SSO provider and Defguard's internal password reset is not needed.
Last updated
Was this helpful?