> For the complete documentation index, see [llms.txt](https://docs.defguard.net/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.defguard.net/1.6/deployment-strategies/gateway.md).
# Adding a location and getting a Gateway token
This documentation will guide you through adding a new location and proceeding with the Gateway deployment, enabling your devices to connect to it via VPN.
## Adding a location in Defguard Core
{% hint style="warning" %}
Please remember that **one gateway corresponds to one VPN location.**
You can also deploy multiple gateways for one location for High Availability.
{% endhint %}
Go to the address you set on `DEFGUARD_URL` with your browser and sign in using the credentials you set up during Core deployment.
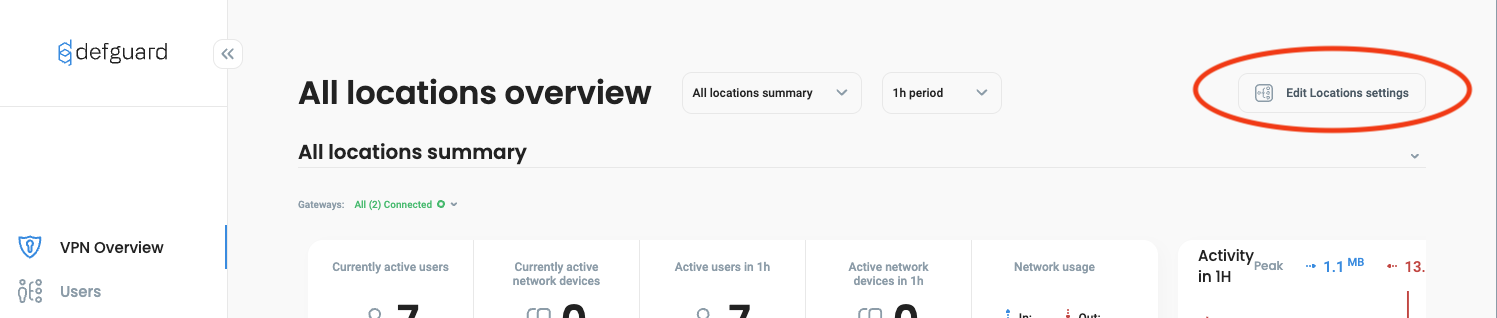
Go to the *VPN Overview* module from the main menu and click the *Edit Locations settings*.
Adding a new location
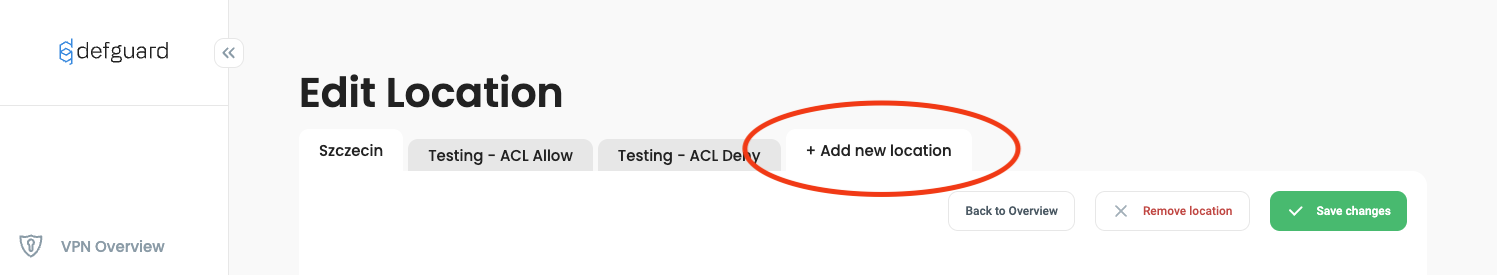
Then click the *Add new location tab*.
Adding a new location
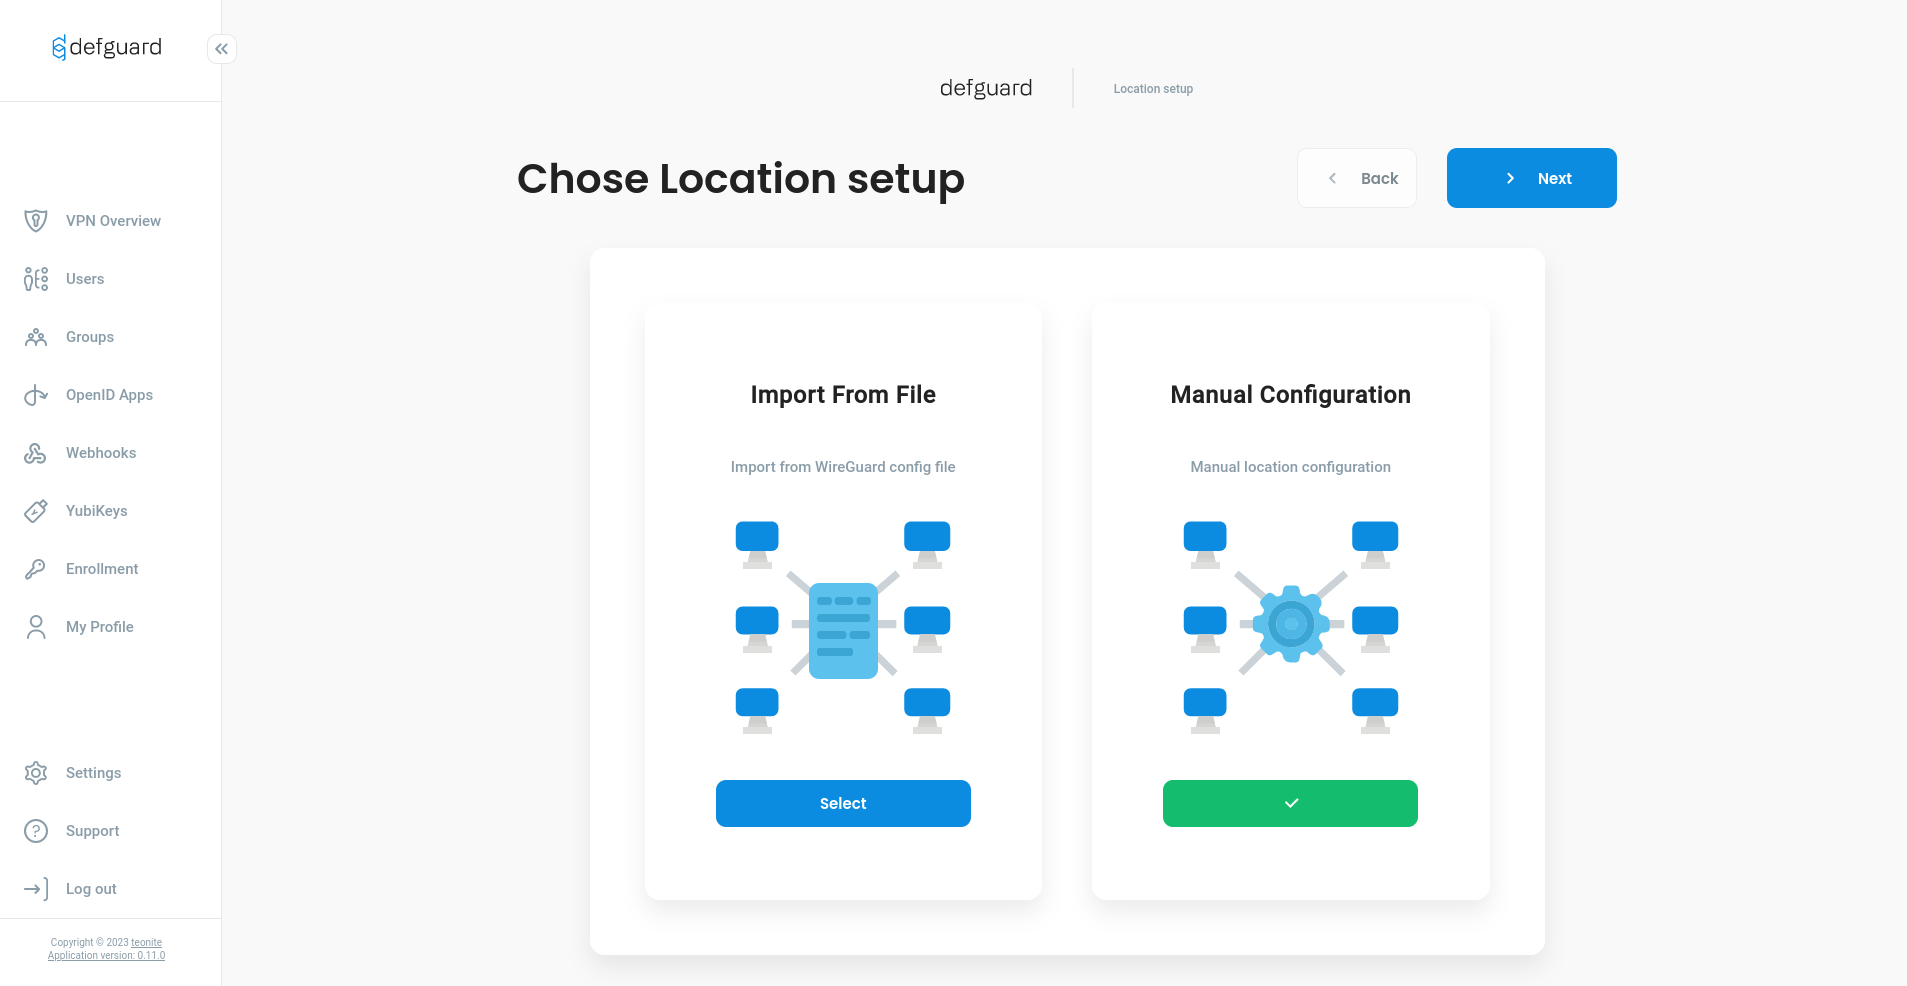
Depending on what is more convenient for you, choose configuration from Wireguard file or do it manually.
Location wizard
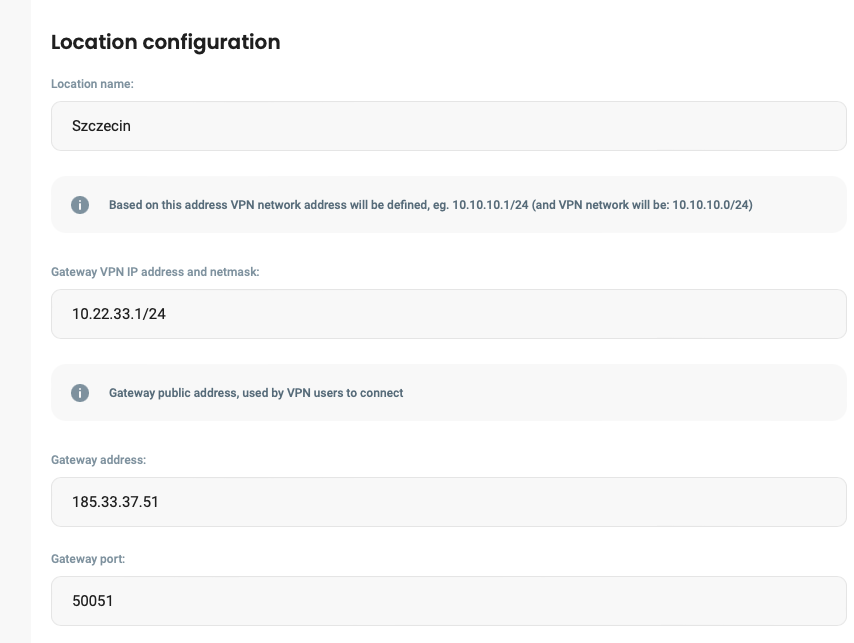
Location configuration
After saving configuration for location you should be redirect to Location overview page, where at the top right corner is `Edit Locations Settings` button, click on it.
Manual configuration
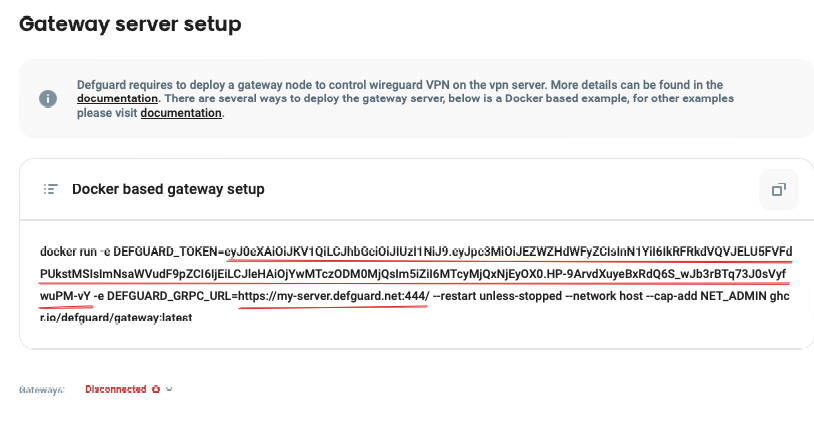
In `Gateway server setup` copy two variables: `DEFGUARD_TOKEN` and `DEFGUARD_GRPC_URL`
Gateway server setup
Also, if core has a custom SSL CA to secure gRPC communication, [you need the CA certificate (more here).](/1.6/deployment-strategies/grpc-ssl-communication.md#custom-ssl-ca-and-certificates)
## Deploy the Gateway service
Proceed with deploying your Gateway service using the selected [deployment strategy](/1.6/deployment-strategies/setting-up-your-instance.md#choose-your-deployment-strategy):
* [package based](/1.6/deployment-strategies/standalone-package-based-installation.md#gateway-1)
* [Docker Compose](/1.6/deployment-strategies/docker-compose.md#deploying-gateway-service)
* [Kubernetes](/1.6/deployment-strategies/kubernetes.md#vpn-gateway-service)
* [Terraform](/1.6/deployment-strategies/terraform.md#gateway-module)
* [AMIs and AWS CloudFormation](/1.6/deployment-strategies/amis-and-aws-cloudformation.md#gateway-instance)
You can also check our guides on running Gateway on [OPNsense firewall](/1.6/deployment-strategies/running-gateway-on-opnsense-firewall.md) or [MikroTik router](/1.6/deployment-strategies/running-gateway-on-mikrotik-routers.md).
If everything went well, Defguard Gateway should be connected to Defguard Core and you can start [adding new devices to your network](/1.6/features/network-devices.md#adding-a-new-network-device).